by Felicien | Jan 4, 2019 | Education
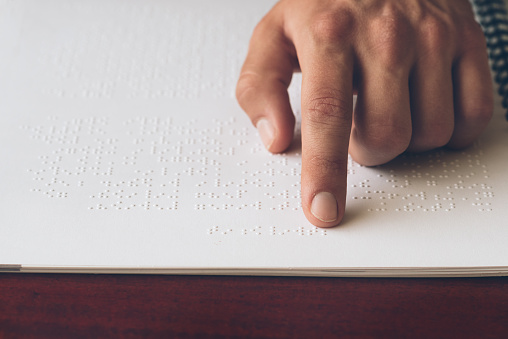
On January 4th, 1809, Louis Braille was born. Louis Braille was a child who lost his vision in an incident involving a sharp tool at the age of 3. During his early life, Louis had an interest in “night writing”, a military code used by the French Army in the 1800s. This “night writing” was a way for soldiers to silently communicate in the dark. At 15 years old, Louis Braille simplified the French soldiers’ code so that it was easier to use and understand. This was the beginning of the Braille System that is still used today.
Braille is a system of raised dots that are felt with fingertips to give blind people a way to read the words around them. The raised dots are arranged in a way that represents letters, numbers, and other characters. There are two different versions of Braille. The first is uncontracted, where each word is spelled out. The second is contracted, similar to shorthand. There is also a type of Braille, the Nemeth Code, that is for working with mathematics.
World Braille day reminds us of the impact that Braille has on the daily lives of people living with blindness. Braille is a key factor in obtaining literacy equality. Without braille, people with blindness or vision loss wouldn’t be able to read anything on their own. Braille helps people to live more independently.
On World Braille Day, further, educate yourself on braille. Learn about all the ways that it makes life easier for those who are blind. You could even join groups that help incorporate Braille into more parts of everyday life.
by Felicien | Jan 4, 2019 | Education
You are driving along and you glance down at your smartwatch. Imagine the horror of it when you hear the sirens wail directly afterward — but you think that can’t be for you: you were not driving over the speed limit. But it can be for you. The police saw you glance at your smartphone, and now you are facing potential license suspension.
It’s here: stricter distracted driving rules in Ontario have the potential to be quite devastating. Here’s what you should know about the new law that took effect on January 1, 2019.
What is the new distracted driving law in Ontario?
The new distracted driving law in Ontario is not necessarily new in the sense of what is considered distracted driving, but new in terms of beefed up penalties. If an officer suspects that you are driving while distracted, then you can be pulled over and cited. The police, however, cannot seize your driver’s license on the roadside. Your case will go before a judge, and upon conviction, you will have your license suspended as well as be subject to fines and demerit points.
What actions are considered distractions according to the new law in Ontario?
When we think of distractions associated with a distracted driving law, we most often think of our smartphones, but there are many other distractions that can result in a conviction. In fact, anything that causes a driver to be less focused on the road is a distraction to driving. The list of distractions according to Ontario’s Ministry of Transportation include the following activities:
Holding an electronic device — like a smartphone, iPad, tablet, iPod, or another device;
Using an electronic device to text, talk, send posts on social media outlets, type in addresses into the GPS or look at maps or control playlists;
Eating; and/or
Reading books or documents.
Further, if you think you can be safe using your electronics at a traffic light or any other time while in stopped traffic, you are wrong. It is not permitted according to this law to use your electronic devices while stopped. You can, however, use the following:
A hands-free electronic device that utilizes technology like Bluetooth and requires you to only turn it on or off; or
A mounted electronic device — whether it’s a phone or GPS system — so long as it is secure and does not move while you are driving.
The only exception to the new law is if you need to contact emergency personnel, like the police, fire department, or medical professionals.
What are the new penalties for distracted driving in Ontario?
Distracted driving has already been an offense in Ontario, but the new law strengthens the penalties to make it more of a deterrent than what it had been. Penalties vary according to the conviction: whether or not you have any prior distracted driving offenses. Plus, aside from the penalties, you can expect your auto insurance rates to increase dramatically. The stakes, therefore, have just multiplied with this new law.
First Distracted Driving Conviction Penalties
For a first distracted driving offense, you can expect the following penalties:
A fine of up to $1,000
Three (3) demerit points
A three (3) day driver’s license suspension, unless you have a graduated license, like a G1- or G2, then the license suspension is for 30 days.
Second Distracted Driving Conviction Penalties
For a second distracted driving offense within five years, you can expect the penalties to double:
A fine of up to $2,000
Six (6) demerit points
A seven (7) day license suspension, unless you are a G1- or G2-license holder, then the license suspension is for 90 days.
Third Distracted Driving Conviction Penalties
For a third distracted driving offense within five years, the penalties increase progressively, and include:
A fine of up to $3,000
Six (6) demerit points
A thirty (30) day driver’s license suspension, unless you are a G1- or G2-license holder, then your license could be canceled — and it can be difficult to get the license back.
Subsequent Distracted Driving Conviction Penalties
For each new conviction, fines and driver’s license suspension increases. You could potentially — if you become a repeat offender — be looking at driver’s license suspension up to two (2) years and fines of up to $50,000.
What to Do When Driving on the Roads in Ontario
There is a reason behind the new law and that is safety. The following are some statistics provided by CAA that you should keep in mind:
“Drivers engaged in visual-manual interactions with cell phones (e.g., texting) are up to eight times as likely to be involved in a crash.” (AAA, 2017)
Twenty-seven percent “of fatal crashes in BC was due to distraction. Police across Canada say that distracted driving has caused more collisions than impaired drivers.” (ICBC, 2016)
Thirty-three percent “of Canadians admit they have texted while stopped at a red light, despite believing it is unacceptable.” (CAA, 2016)
These are serious statistics. The obvious way to prevent the above from happening and from you obtaining a distracted driving citation and subsequent conviction in Ontario is simple: don’t use your electronic devices while driving, but also, don’t eat, read, or write, or even groom yourself by putting on makeup or brushing your hair. Refraining from these activities can help bring down the above statistics and can help make our roads safer.
by Felicien | Jan 4, 2019 | Education
There was something of a cultural shift in the technology sector during 2018 that will undoubtedly impact 2019. Up until last year, cybersecurity issues seemed to predominately plague significant corporations and organizations. The Democratic National Committee hack fallout and Russian bots on Facebook were coupled with big-time breaches at Equifax and others that garnered headlines. Even the recent reports coming out of U.S. intelligence agencies point to enemy states such as China and Iran stealing American intellectual property.
Cyber threats ramped up in 2018 and the World Economic Forum ranked technology breaches as a top risk to economies worldwide.
“Attacks are increasing, both in prevalence and disruptive potential. Cyber breaches recorded by businesses have almost doubled in five years, from 68 per business in 2012 to 130 per business in 2017,” the Forum reported.
Consider for a moment that climate change and severe weather events such as hurricanes and tsunamis were also listed. That should put the danger in context for any business leader. And that’s why the mainstream perception about breaches has shifted significantly.
These days, small and mid-sized companies recognize that their personal information and critical data are targeted at a much higher rate than Fortune 500 outfits and national-level organizations. Ransomware has emerged as an almost routine method to extort money, and now fraud from crypto-mining is trending high. Business owners and decision-makers are prioritizing cybersecurity because the stakes are just too high. Cyber threats are likely to escalate during 2019, and these are some dire predictions.
1: Strict Data Breach Fines
Last year, regulations such as the California Consumer Privacy Act implemented harsh penalties for companies that fail to protect personal employee data. The conventional wisdom is that businesses and non-profit organizations alike have a responsibility to safeguard the information they ask of team members.
Cyber attacks that penetrated Uber, for example, reportedly resulted in the transportation organization settling out of court to the tune of $148 million as a result of a 2016 breach. Leading online companies such as Facebook and Equifax have been under fire and they both reportedly were fined a maximum penalty of £500,000 in the UK.
Currently, Google, British Airways and Facebook once again are under government scrutiny for cybersecurity failures and hefty fines could be coming. While this may not seem like a direct and discernible danger to small and mid-level outfits, think again. Although household-name organizations make headlines, everyday companies can expect to get hit with penalties for lack of cybersecurity as well. The moment a company asks employees to provide personal information, that organization becomes responsible for protecting it.
2: Rise of the Machines
The days of a rogue hacker halfway around the world infiltrating a system are expected to evolve in to (artificial intelligence) AI cyber attacks. If this sounds a lot like the sci-fi “Terminator” movie franchise, that’s not far from the truth.
Hackers are expected to deploy machines under their control to more rapidly and covertly penetrate business systems and cull valuable information. But beyond mining, these human-controlled devices will increasingly have the ability to impact the lives of everyday people.
Consider that the IoT continues to create an accessible matrix that can be manipulated. Autonomous vehicles, smart-home technology, and even friendly Alexa are being weaved into the fabric of human lives. This opens the door for hacker-driven AI to penetrate lives outside of the workplace. The necessity of cybersecurity in our personal lives is expected to grow exponentially going forward.
3: Governments Expected to Ramp Up Cyber Weapons
The mainstream media has been brushing up against the subject of enemy states attacking infrastructure such as power grids. It goes without saying that governments across the world are not sitting idly by as others hone their hacking talents.
From voting booths to water supplies, governments around the world are expected to meddle more and more in each other’s affairs. When someone loses, expect malware, ransomware and debilitating viruses to be unleashed.
While your small or mid-sized company may not be the target of a rogue state attack, it could end up being collateral damage. Don’t be taken by surprise, secure your company and personal data before the first wave hits.
4: Email Expected to Remain Top Data Breach Vehicle
Criminal hackers view email as the gift that keeps on giving. New hires tend to need time to understand the protection protocols around email usage. And, too many outfits lack adequate policies or fail to update usernames and passwords effectively. Employee email has ranked among the most vulnerable backdoors into an organization’s sensitive data and the best way to deploy ransomware.
Even though cybersecurity and IT teams warn decision-makers about the dangers of sub-par email protections, it is expected to remain a primary threat in 2019. Every day companies cannot take email security seriously enough in 2019.
5: Tougher Laws and Regulations Expected
The 2018 U.S. congressional hearings that involved Facebook, Google and others demonstrated that lawmakers recognize that cyber threats are prevalent and current regulations appear inadequate. Intellectual property and critical data are now outpacing oil regarding value.
In the U.S., states are creating more stringent laws to deal with hacking. The federal government and countries abroad are also wrestling with policies to manage cyber threats. It’s essential for small and mid-sized outfits to follow the trend and communicate with lawmakers at the local, state and federal level. The laws that come out of cybersecurity hearings are likely to impact the business community in a significant fashion.
by Felicien | Jan 4, 2019 | Education
Only a few short weeks ago, we wrote about the introduction of WordPress 5.0 in early December and discussed whether or not your company should upgrade now, never or at a later date. Our recommendation was to wait until some of the bugs had been worked out of the system and until your business has a slow time of year to ramp up to the new way of posting with this new update. It seems that we were on the right track since WordPress has just made WordPress 5.0.2 available to the public, a maintenance release that addresses 73 known bugs associated with WordPress 5.0.
What is WordPress 5.0.2?
WordPress 5.0.2 seeks to address some of the problems that users have been having with the new WordPress 5.0 release. Most of these issues are associated with the block editor feature. Unlike previous WordPress releases, 5.0 is a WYSIWYG editor and requires no HTML or coding knowledge. According to WordPress, the new maintenance release increases the posting speed by 330 percent (for a post with 200 blocks). It also includes 45 block editor improvements, fixes 17 known block editor bugs and addresses some internationalization issues. You can view a complete list of the problems discussed with 5.0.2 on the WordPress website.
Should we upgrade to WordPress 5.0.2?
Our original opinion on whether to upgrade to WordPress 5.0 now or wait still stands. We still feel it’s prudent to expect since many businesses are otherwise occupied with end-of-the-year tasks in December and January and a radical revamping like 5.0 is likely to have a few growing pains. Also, 5.0 uses Gutenburg, which is not compatible with many WordPress plug-ins. As with any upgrade, we also recommend backing up all of your WordPress files before you download WordPress 5.0.
However, if you have already upgraded to WordPress 5.0, it is a good idea to go ahead and download the 5.0.2 maintenance release. This is likely to make your WordPress experience less troublesome and less time-consuming. To upgrade to WordPress 5.0.2, download WordPress 5.0.2 or go to your WordPress dashboard, go to Updates and click Update Now. In fact, you may already have the new maintenance release. Websites that support automatic background updates have already started to update automatically.
To learn more about using WordPress, deciding whether WordPress 5.0.2 is the right choice for you and your company, and to learn ways to make your website more efficient for both you and your readers, contact Ulistic.com or call us at (enter contact info). We can also help you with backing up your data before your upgrade.
by Felicien | Jan 3, 2019 | Education
In April of 2018, South Carolina became the first state in the nation to require insurance companies to establish data security standards to protect consumers from the consequences of cyber attacks. The legislation named the Insurance Data Security Act, also put requirements in place for how insurance companies must investigate cybersecurity attacks. South Carolina insurance carriers have until July of 2019 to fully implement the Insurance Data Security Act. The law officially went into effect on January 1, 2019.
State legislators drafted and passed this new law in response to a series of recent attacks in the insurance industry that exposed the private demographic and financial data of millions of Americans. The 2015 attack on the insurance giant Anthem appears to be the most significant catalyst for initiating and enforcing the new regulations.
What the Insurance Data Security Act Means for South Carolina Insurers
Under the provisions of the new security act, insurance companies, agents, and all other licensed entities that conduct business in South Carolina must establish a comprehensive security program and put it in writing by July 1, 2019. As quoted from state legislation, the new security program must “commensurate with the size and complexity of the licensee, the nature and scope of the licensee’s activities, including the use of third-party service providers, and the sensitivity of the nonpublic information” within the control, possession, or use of the licensee.
Additionally, South Carolina insurers must base the company’s cybersecurity program on individual assessment of risk. Based on these results, the licensee must design an information security risk that reduces these risks as much as possible with the stated goal to completely eliminate the risks. It is the responsibility of each insurance licensee to determine appropriate measures related to the following:
Access controls
Cybersecurity event audit trails
Data
Device
Encryption of nonpublic information at rest on removable data and mobile devices
Encryption of nonpublic information in transit
Multi-factor authentication
Personnel inventories and mapping
Physical access restrictions
Routine system and testing monitoring
Secure application development practices
Secure disposal of all nonpublic information
Systems upgrades
This is a significant undertaking for insurance companies and agents in South Carolina to achieve in the next six months. Many will find that they need to reach out to information technology specialists to help them come into compliance in the time required under state law.
Requirements for Insurance Company Director Boards
The Insurance Data Security Act not only imposes what insurers must do to implement a plan to safeguard consumer privacy, but it also dictates required actions for people with specific roles within the company as well. For example, the board of directors of each insurance company in South Carolina are personally responsible for supervising the development and implementation of the new cybersecurity program. Supervising duties of the board also include issuing a directive to senior management to produce an annual written report that contains the following information:
A high-level overview of the cybersecurity program status and whether each agent or licensee appears to be in full compliance with the new program.
All material matters to include individual cybersecurity events and the response to each, risk assessments, risk management decisions and controls, service provider arrangements with third parties, and results of all testing. Most importantly, senior management must recommend specific changes to the program in response to any ongoing issues they have observed that have posed a challenge to compliance.
It is crucial to the success of the new cybersecurity program that board members and senior officials with South Carolina insurance companies take their role seriously. This is the only way to ensure successful implementation of the program as well as address any early compliance concerns.
Specific Licensee Requirements under the Insurance Data Security Act
The act also spells out highly specific responsibilities for insurance licensees. For example, every licensee in the state should have produced a written document outlining a plan on how to respond to and recover from a cyber attack. This covers attacks that threaten the security of any nonpublic information that the licensee retains on his or her person or within the company’s computer information systems. These plans were due by January 1, 2019, and must contain all of the following information:
The process of internal response to a cyber attack
Specific goals for the prevention and response plan
An outline of the specific responsibilities and roles of each person who has the authority to make cybersecurity decisions
Internal and external communication and sharing of information
Requirements for remediation
Detailed documentation of any recent cyber attacks, including each step of the response
Any revisions made to the plan since its original creation date or any anticipated future changes
The new law gives licensees until July 1, 2020, to create and implement a cybersecurity program with a third-party service provider. The expectation is for licensees to choose the provider using due diligence. It is the responsibility of licensees to ensure that the new service provider possesses the ability to offer administrative, physical, and technical support as required under the provisions of the cybersecurity act. This is necessary to ensure that third-party service providers protect computer systems as well as all nonpublic customer information.
Finally, the licensee must regularly monitor the work of the service provider to ensure compliance. Upon discovery of any issues, the licensee must initiate adjustments to the agreement between the two companies. The new law makes it incumbent upon every insurer in South Carolina to provide an annual compliance certification as well.
Protocol for the Investigation, Response, and Disclosure of Cybersecurity Attacks
Insurance companies, along with agents and licensees, now have only three business days after a discovery to investigate and report the events surrounding a cyber attack or event. The definition of a cyber event includes any action that resulted in an unauthorized person gaining access to nonpublic information. The purpose of the cyber attack is to disrupt computer systems to make it possible to obtain and misuse the information stored inside of them. The definition does not include any data that a cybercriminal destroyed or returned.
The Insurance Data Security Act includes a somewhat vague definition for what qualifies as nonpublic information. For example, protected data includes anything that usually receives protection under existing laws for data breach notification. However, it does not define the specific types of data.
Other information protected under this new act include any business data that demonstrates proof of unlawful tampering by an insurance licensee. This consists of any unauthorized disclosure of information, use, or access that demonstrates the licensee attempted to manipulate data for the benefit of the insurance business.
Once a licensee has determined that a legitimate cyber event occurred, it is up to him or her to initiate an immediate investigation. The investigation must include each of the following elements:
Determining whether the incident meets the legal definition of cyber event
Researching the facts regarding the event
Determining whether a cybercriminal obtained any nonpublic data and identifying the customers impacted
Promptly restoring any vulnerabilities that caused the breach of data
Both insurance licensees and third-party service providers must retain a record of all cyber events for a minimum of five years. They must also produce the record promptly when any authorized party requests to see it.
About disclosure of cyber events, a licensee must notify the Director of the Department of Insurance within 72 hours of resolving the issue. This requirement covers all insurance businesses licensed in South Carolina. Additionally, the act requires licensees to notify another government agencies or insurance supervisory boards if the data breach involved more than 250 state residents or a reasonable likelihood of widespread harm exists. The notification to the government agency or insurance supervisory board should include the following information at a minimum:
The date and specific details of the cyber event
The methods used to discover the issue
The types of nonpublic data compromised
Whether the licensee notified law enforcement, and if so, the data this occurred
The intended steps of remediation
A valid copy of the most recent privacy policy of the licensee
The specific plan for investigation and notification of consumers
Other States Expect to Follow Suit
South Carolina has taken a significant step toward consumer protection by implementing this law as of January 1, 2019. Several other state legislatures are currently considering the same or a similar act, so it should come as no surprise to consumers and those in the insurance industry to see widespread adoption in the future. Even industries outside of insurance may look to the act to determine its usefulness when adapted to that specific industry.