by Felicien | Jun 26, 2018 | Education
Have you ever used public Wi-Fi in a coffee shop? – In a hotel? – While sitting at an airport waiting for your flight?
We’ve yet to meet a remote worker who can say “no” to all of these questions. Running a business means being a road warrior and using public Wi-Fi from time to time.
However, there are precautions you should take when using public Wi-Fi. Just a single visit online in a coffee shop or airport terminal can put your confidential data at risk. “Free” doesn’t always mean safe. With viruses, malware, and hackers just waiting to infect your laptop, working remotely can be like navigating a minefield.
The following are four tips to help you work securely when using public Wi-Fi.
Tip 1 – Avoid Crowded Cafés
We’re in the midst of a workforce revolution. People no longer want to be tied to their desks. And if you need help finding a space that offers fast Wi-Fi, plentiful workspace, and outlets, there are a number of new sites and applications that rate businesses on these things and more.
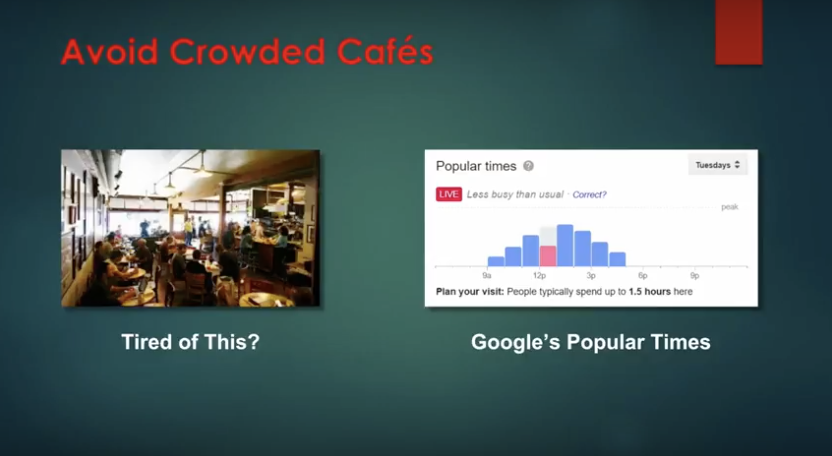
Try Google’s Popular Times Feature – Plug in the name and location of your café, and the hours you’d like to visit, and Google will let you know how busy it is. Since introducing the Popular Times feature in Google Search and Maps in 2015, we can now determine how busy a particular site is during different times of the day, and days of the week.
Even better – Google updated this “popular” app to add a real-time look at how crowded a café is. This is a great tool if you want to lessen the chance that someone sitting at a table too close to you will eavesdrop on your email messages and browsing.
Tip 2 – Find New Places To Work Online
If your local café is too crowded, you may want to find another place to work. However, you need one with adequate space, power outlets, and Wi-Fi bandwidth. There are a number of new sites and apps you can use to help you find just the right place for you.
WorkFrom.com
WorkFrom’s mission is for work/life betterment in an office-optional economy. They want to help people everywhere find and share trusted spaces to work remotely. It’s the world’s largest recommendation website for trusted spaces to work remotely. Its database spans more than 300 cities and towns. You can download it from the Apple App Store or from Google Play.
WHA by Work Hard Anywhere
This is an iOS app that you can download to your iPhone from the Apple App Store. It uses your iPhone to give you nearby, work-friendly spots where you can use your laptop. You can apply filters to rate Wi-Fi speeds, the number of outlets, workspace size, parking, bathrooms and more.
Tip 3 – Stay Secure
Hackers take advantage of your thirst for Wi-Fi by creating networks that have legitimate-sounding names so you’ll be fooled into logging on. These are called rogue hotspots. They are typically located in airports and other busy locations. Always double check with a manager to determine if the Wi-Fi you choose is a safe hotspot.
Take note: Even official public Wi-Fi’s can be compromised. So, it’s always best not to do any banking, bill paying or shopping over public Wi-Fi.
Always look for websites that have “https” before sending any personal information. Also look for a small lock icon in your web browser that indicates the website is safe. You can use a virtual private network (VPN) to add an encrypted layer of protection for your data to pass through. You can try free ones like CyberGhost VPN, or paid ones which tend to be faster like HotSpot Shield Elite or proXPN.
CyberGhost VPN is mostly free and totally safe. Some of the aspects are free; others aren’t. It’s also very easy to use. With it, you can surf anonymously, unblock streaming and other websites, and protect your Internet connection from being tampered with while using public Wi-Fi. Although a VPN isn’t appropriate for time-sensitive gaming, it can figure out if and where it can direct you to stream services such as news or movies. Many other VPNs can’t do this.
HotSpot Shield Elite is a subscription-based service that allows you not only to secure your connection while surfing on public Wi-Fi, but it also lets you access sites not normally available when you’re outside of the U.S. (such as Pandora and Hulu). It’s the paid version of Hotspot Shield with faster and more stable streaming.
proXPN VPN lets you surf the web securely via public Wi-Fi or when you’re at work or home. They offer a lifetime premium subscription that provides unlimited bandwidth via their ultra-private global server network. You can surf with complete anonymity. proXPN will even unblock geo-locked content so you can browse freely from anywhere in the world with an Internet Wi-Fi connection. And they say it never logs your online movements so others can’t track or steal your confidential data. proXPN VPN got a 4-Star Rating from PC Magazine.
Tip 4 – Stay Private
It can be difficult to remember that when working online in public, your screen and everything you do can be seen within eyeshot of strangers. There’s a term for this – it’s called “Shoulder Surfing.” Always pay attention to where you sit and who’s nearby.
One way to protect yourself is by using a laptop privacy filter. You simply slide it over your screen. It limits the viewing angle to only straight on. Also, be sure to dim your screen’s brightness setting. The lower the brightness, the more effective the privacy filter will be at narrowing the viewing angle.
Do you feel like you can’t win when security risks are coming at you from all directions? We understand, and we can help. We’ll do all we can to protect your confidential data and your business. Partner with our cybersecurity experts for the safeguards you need.
by Felicien | Jun 26, 2018 | Education
Best Way to Improve Cybersecurity? Train Your Employees!
Why an informed team is your organizations best defense against cybercriminals
Cyber attacks and data loss are the last thing any organization wants to fall victim to. In an increasingly digital workforce, companies are investing in all kinds of cybersecurity efforts to ensure the bad guys can’t invade their business network. This kind of security is even more important in professional services industries like finance, law and government. The more sensitive the data, the more cybercriminals want it.
The world of Information Technology is definitely evolving and rising to meet the increasing threat. However, even as technological solutions and regulatory standards are developed, the cybercrime landscape is increasingly sophisticated and complex.
Particularly, preventing cybercrime can be incredibly difficult considering the vast majority of cybersecurity issues occur as a result of human error. That’s right. Your very own employees should be your number one concern when tightening cybersecurity. Even worse? These internal threats can be very hard to identify and address because they’re so pervasive and widespread. The bottom line is that without a ‘cyber-literate’ team, your business network will always be open to increased threat.
How An Educated Team Helps Secure Your Network
Helping your staff become and stay ‘cyber-literate’ is critical based on the very fact that most cases of data breach and loss result from an employee’s lapse in judgment. Whether the internal threats you face are malicious – like a disgruntled and spiteful worker – or more benign – like an employee who struggles with basic email technology – facing them head-on is critical.
Minimizing human errors like downloading malicious files or clicking a malicious link can make a world of difference in reducing your vulnerability to cybercrime. So, what’s the best way to minimize human error? Educate and empower your team to be their own cybersecurity experts. Without driving awareness and understanding, your team will never be truly prepared. Take the reins and help your team better identify, respond to and report suspicious cyber activity.
Not Just a Security Boost: How Security Awareness Training Improves Employee Morale and Retention
The really great thing about security awareness training is that it really isn’t just about tightening security. Taking the time to invest in security awareness training for your staff can be a major team-building and morale-boosting initiative. Offering your team specialized training and professional development helps you communicate just how valuable they are to your organization. Even better, it makes them want to stick around – meaning your employee retention rates will be nurtured.
You may be asking: how in the world does security training make my team more committed and loyal. The answer is simple: when you include your team in mission-critical tasks, they know they’re important and valued pieces of the puzzle. It really is that simple. If your employees feel valued, included and taken care of, they will be better advocates for your organization as a whole. This means they’ll be more committed to realizing objectives and making sure the company has all its bases covered.
Plus, it doesn’t hurt that security awareness training can be an exciting break from the boring and mundane tasks of the regular workday. Who doesn’t want a job with a little bit of excitement built in? By working with your team to research and understand cyber threats – both internal and external – your team gets to focus on something new and out-of-the-ordinary. You can even let your team spearhead initiatives and stage simulation attacks to keep co-workers on their toes. Make it even more fun by creating internal competitions or offering incentives. Do whatever it takes to help your team become the masters of the technology they use day in and out.
Overall though, the biggest benefit of security awareness training for your staff is the overall improvement of your organization’s success. With a happy, informed and productive team, your network is safe and more secure from threats of all kinds. Undertaking an educational and fun team approach to cybersecurity really makes all the difference in producing positive and lasting results. Don’t leave your cybersecurity discussions limited to manager meetings behind closed doors. Involve your team, ask for their input and make sure everyone is on the same page. This is a surefire way to keep your team feeling valued and your company successful.
Empowering your Team: Tips for Effective Security Awareness Training
So, it seems like a no-brainer: get your staff well-versed in cybersecurity objectives and all will be well, right? This is true, but it’s critical to go in with a plan. Creating an effective security awareness training program for your team means you must keep a few baseline suggestions in mind. Using these suggestions as a starting point will help you develop a custom-tailored plan to meet the needs of your business and ensure all your cybersecurity concerns are shared with your team.
Check out these preliminary suggestions for effectively training your team in all things cybersecurity:
Know Your Weak Spots
The first step is knowing where exactly you need your team to be extra vigilant. Are email phishing scams your biggest concern? Do you need your team to be more careful with sharing access control data? Whatever your weak security spots are, be sure to identify them and discuss them transparently with your team.
Avoid Doom and Gloom
Of course, you want to make sure your team is aware of the threats you face, but the last thing you want to do is scare them into silence or make them constantly dread an impending security crisis. As much as possible, keep it light and keep it fun. Avoid the doom and gloom and find ways to make this a team-building exercise instead of a divisive warning.
Empower Your Team
The best thing you can do when working to train your staff in all things cybersecurity, is to let them lead the charge. Ask their opinions about various threats. Allow them to offer strategic suggestions and provide their input. The more you empower your team to take initiative, the better they will be at protecting data on the frontlines.
Consult an Expert
Another great suggestion when undertaking security awareness training for your team is to check in with a local team of IT security experts. If you’re wondering how to start and what you should focus on, consultation with a strategic IT partner can make all the difference in getting you and your team on the right path. IT professionals have the experience and expertise to help you build a strong internal cybercrime defense.
No matter what industry you’re in, helping your team better understand cyber threats and strategies for mitigation is critical to the success of any modern business. The last thing you want is for one of your team members to inadvertently welcome cybercriminals into your network. You really don’t have to live with this constant fear. Take the initiative to get on the same page as your team – let them know the threats you face and empower them to take action in anyway you see fit.
Once you have your own team prepared and in your corner, you’ll be better able to take on any cybercrime battle that comes your way. Consult with a team of professionals to find out exactly what you and your team should be doing to stay secure.
by Felicien | Jun 26, 2018 | Education
New Office app is a scheduling game-changer for managers and employees
If there’s one thorn in the side of every business, it’s mastering an efficient and functional schedule for the whole team. Between various levels of employees, diverse job types and differing time allotments, making a consistent and easy-to-access schedule can be a huge challenge.
Of course, in the increasingly tech-based work world, countless companies are arriving on the scene claiming to have the newest and best scheduling solution that your company MUST take advantage of. Listen, there are some great stand-alone solutions out there, but often the big promises offered don’t measure up. Even worse, what good is a scheduling solution if it isn’t integrated with all the other applications you already use for calendar tracking and communication?
That’s why business professionals of all kinds are excited about the latest app from Microsoft, called StaffHub. StaffHub is truly changing the game for scheduling in the workplace and the best part is, the application is designed with Microsoft’s familiar and functional signature touch.
Tell Me More: What Exactly is StaffHub?
StaffHub is the latest productivity application released for Office 365. The application is designed specifically to better connect staff and managers to the critical scheduling data they need each day. The application is all about easy access, easy modification and easy communication to ensure that the team is always on the same page and scheduling conflicts are put to rest.
Check out some of the BEST features that StaffHub provides:
Easy Schedule Creation and Sharing
Managers are able to easily create schedules and share the content with their employees seamlessly. The StaffHub app and its data can be accessed from any mobile device through the Office 365 app. Gone are the days of the printed schedule on the wall of the office. With StaffHub, workers can simply open the app to see their upcoming scheduled shifts.
Supreme Schedule Display and View Options
Not only is the schedule easier to create and access in the app, StaffHub makes it look better too! Say goodbye to scratched out times and names on your paper schedule. The StaffHub schedule appears on an attractive and organized grid that can be color-coded for ease. There are also many different viewing options. Users are able to switch between monthly, weekly, or daily views and tapping on an individual shift shows more details. There’s even an option to view the total scheduled hours for each employee.
Streamline Shift Switches
Ah, a manager’s worst nightmare. You spend hours creating a schedule only to get three different employees at your door requesting changes. With StaffHub, this nightmare ends now. When scheduling conflicts come up, StaffHub makes it easy for workers to request a switch. Simply tap the shift in question, select the person to switch with and voila! A request is sent directly to the manager for final approval. This way, you stay in constant control of your schedule while keeping your team happy and organized.
Integration and Communication
As mentioned, there are a lot of stand-alone apps that promise a revolutionary scheduling solution. However, StaffHub is unique in that it is entirely integrated and compatible with Office 365 apps – making communication and collaboration a breeze. Employees can exchange messages and access other content through the StaffHub app. Even better? StaffHub is compatible with Azure Active Directory, meaning managers can add and remove team members as necessary.
Streamlined Success: StaffHub Makes for Happy Managers and Content Staff
Overall, StaffHub is a great tool for streamlining processes and keeping your entire team on the same page. When team members are able to easily understand what is expected of them and access the critical data that they need, jobs get done quicker and employees are more motivated to work. While countless providers are on the market claiming to be the productivity powerhouse, it’s a good idea to peek at what you may already have included in your Microsoft Office 365.
By taking a look at your existing infrastructure before you commit to any applications or solutions, you’ll have a better idea of what specific features you need and how to revamp your tech solutions accordingly. Microsoft has been on the scene for decades – working constantly to keep up with the times and give business users the solutions they truly need.
For Office 365 users, StaffHub is hands down, the no-brainer solution for scheduling. Integration, ease of use, productivity and presentation—what more could a scheduling manager ask for?
Looking to get on top of your scheduling practices? Tired of shift-change nightmares and hardcopy schedules taped up in the breakroom? Reach out to a local team of IT experts for consultation on your best options for schedule management. A team of professionals can help get you on the right path to choosing apps that work better for you and your team.
by Felicien | Jun 25, 2018 | Education
Ohio Fire and Police Departments Latest to be Hit by Ransomware Attack
US Secret Service investigates after second ransomware infection in a month
In April of this year, news broke of a devastating ransomware attack at Riverside Fire and Police Department in Ohio. The attack halted operations and over ten months’ worth of data relating to active investigations was encrypted by criminals. The emergency service department’s server was said to be infected through malicious correspondence, disguised as a legitimate email fax.
Luckily, in response to the first attack, the Riverside Fire and Police Department did not pay the ransom, setting a great example for other ransomware victims across the country. The emergency service departments managed to recover most of the critical data from existing backups and public court records. However, the extent of the attack left the Fire and Police departments unable to restore their systems completely.
Doubling Down: Riverside Fire and Police Department Gets Hit by Second Virus
Even worse? The cybersecurity trouble didn’t stop there for the Riverside Fire and Police Department. Less than a month after the initial attack – just as the departments were getting their bearings –cybercriminals struck again and infected Fire and Police servers with a second ransomware outbreak. However, since the departments were on guard from the first attack, their team was more prepared to respond to the second infection.
News of the second attack broke in early May when the US Secret Service was summoned to Ohio to lead a cybercrime investigation. Luckily, department officials had learned from the first attack and had begun backing up data daily. Thanks to this proactivity, the second attack was only able to hold about eight hours of work hostage and the Fire and Police Department was able to recover quickly and fully after the second attack.
However, just because the second attack wasn’t as bad, doesn’t mean it didn’t have a negative effect on productivity at the emergency services department. City Manager, Mark Carpenter claims that though more proactive backup measures had been taken, rebounding from the attack still resulted in redundancies.
“Everything was backed-up,” Carpenter said in an interview. “But we lost about eight hours’ worth of information we have to re-enter. It was our police and fire records, so we just need to re-enter the reports.”
US Secret Service agents are taking the attack very seriously, commencing an extensive investigation. Secret Service agents hope to determine specific points of entry – not just for this attack but for the initial attack as well. The investigation will hopefully uncover critical clues that will help officials track down and stop the hackers once and for all.
A Startling Reminder: No One’s Digital Data is 100% Safe!
These repeat attacks on the Riverside Fire and Police Department serve as a critical reminder that emergency service departments are increasingly becoming victims of ransomware attacks and data loss. In fact, many recent ransomware attacks on emergency service departments have been more devastating than this year’s attack in Riverside. Last year, the Cockrell Hill Police Department in Texas was hit with a massive ransomware attack, resulting in the loss of nearly eight years’ worth of investigation data and evidence.
It doesn’t stop there either. Recent attacks on emergency service departments have been reported across the country. Most recent reports include attacks in Illinois, Massachusetts, Oregon, South Carolina, as well as additional attacks in Ohio and countless others from coast to coast.
However, it must be noted that there’s no evidence to suggest that cybercriminals are specifically targeting emergency service departments. Rather, these attacks do suggest that the bad guys are attempting to deploy more enormous and wide-reaching phishing campaigns in hopes of hitting as many targets as possible. Using manipulative social engineering strategies on a large pool of potential victims, improves the chances of duping targets and infecting as many servers as possible.
If Cyber Criminals Can Breach a Police Station, How Safe is Your Company Data?
While emergency service departments are often able to bounce back quickly – thanks to reliable backups or quietly paying off ransoms – this increase of ransomware attacks emphasizes the need for security awareness training, even for the most seasoned of investigative departments. More importantly, these attacks also serve as a crucial reminder for everyday business professionals. If police and fire departments are falling victim to ransomware attacks, even with the best firewall and cybersecurity measures in place, regular business owners should be on much higher alert.
No matter how extensive your company’s cybersecurity efforts may be, phishing attacks are increasingly being designed to sneak past filters and firewalls. Therefore, getting proactive must be prioritized in your cybersecurity toolkit. Phishing scams are now the most common and effective mode of malware attack and in turn, training your frontline workers to identify these attacks right away and respond to them effectively is critical to keeping your data safe.
Security awareness training is often cited as the best means of preparing front-line tech users to identify and respond to malicious cyberattacks. After all, an informed and vigilant team is a business’ best defense in an increasingly hostile and sophisticated cybercrime climate.
Preparing for the Worst-Case Scenario: What is Security Awareness Training?
Security awareness training isn’t just about reading up on the latest attacks and teaching your team the definitions of phishing, malware, and ransomware. Truly proactive security awareness training involves detailed and interactive modules that help users get a hands-on experience. This includes throwing your team into realistic attack simulations to help them identify red flags and respond with finesse.
So how do you ensure the training you’re providing to your team is up to snuff? Consult or partner with an expert in cyber security. Today’s managed IT service providers are current on the latest cyber-threats. They can assess your current security to see if it’s powerful enough to stop all attacks. In addition, a good IT professional will recommend customized security solutions that can fortify your organization against the ongoing attacks. As the world moves forward, protecting our priceless data is fast-becoming a number one priority.
by Felicien | Jun 25, 2018 | Education
Cyber Hacks on DNA-Testing Companies Raise Fears about Genetic Data Privacy
DNA-testing companies the latest to be targeted by cybercriminals
Stories of businesses getting hacked by cybercriminals are pretty much par for the course nowadays. Increasingly, companies who collect and store large amounts of user data are prime targets for malicious and greedy hackers. From social networking sites to ride-share companies, large stores of user data are one of the hottest commodities on the cybercrime market.
MyHeritage hack: Over 90 million users affected
One of the most recently reported attacks saw the email addresses and passwords of roughly 92 million users hacked. MyHeritage – an international company based out of Israel – is a DNA testing provider that offers customers the unique experience of determining the specific makeup of their ethnic ancestry and lineage. The MyHeritage hack stands out among others for the very obvious fact that the company doesn’t simply collect basic user info like emails and passwords – it collects and stores mass amounts of genetic DNA from subscribers.
Now, it must be noted that the MyHeritage attack only saw the theft of user emails and passwords. According to the company, none of the genetic data and DNA information provided by customers was compromised. Nonetheless, the attack serves as a critical reminder that nearly any kind of data stored on servers is at risk of being hacked.
The hack – which occurred in October of 2017 – was only identified and reported to the company by a security researcher seven months later in early June of this year. With about 92 million users affected, MyHeritage has been in damage control mode ever since. While representatives for the company claim there is no evidence to suggest the attack was malicious, they’ve admitted they can’t know for sure.
No genetic data affected, but can it be protected?
It’s important to remember that none of the genetic data collected by MyHeritage was hacked. In fact, most genetic data is stored separately and organized anonymously using a numbered barcode system. However, as cybercriminals continue to become more sophisticated and as user data becomes more valuable, companies will be required to work harder to keep even seemingly secure data safe. Especially when the data being collected includes genetic profiles of users.
MyHeritage has been taking steps to tighten cybersecurity protocols and increase user-controls and account security settings. A forced password change for the nearly 100 million affected users arrived by email. Additionally, the company has facilitated two-step verification controls to ensure user logins are better managed. However, some experts argue that this could have been set-up proactively to mitigate hack risks ahead of time.
Rob Verger, the Assistant Tech Editor at Popular Science Magazine raised a valid point in a recent interview. “If they can’t protect user data,” Verger said, “what makes them able to protect the genetic data?”
Going digital: Balancing benefits with risk in the modern marketplace
There’s a balancing act to be done when considering cases like these. There’s no denying that the electronic storage of data has been an asset – especially to the health and sciences industry. Doctors across the nation are making moves to paperless Electronic Medical Record (EMR) systems that make the patient experience more efficient and organized. Genetic testing companies have been revolutionary in their ability to efficiently and privately connect customers with priceless genetic information.
So how do you know when to draw the line? How can individual consumers reap the benefits of these technologies without leaving themselves open to invasions of privacy? According to Verger, the best strategy when giving out personal data is caution and a second thought.
“People should be careful about the types of information they give these services,” Verger said. “If your biggest nightmare is having your email address all the way to your ethnic history being hacked, then you shouldn’t subscribe to these companies or provide data.”
At the end of the day, what matters most is how the users were affected and how MyHeritage responded. When it comes down to it, users have a right to be wary. Not only about the attack, but also about the incredibly long time it took for the hack to be identified and disclosed to users.
Identification by a security researcher, seven months after the fact is hardly what anyone would call a vigilant cybersecurity effort. While MyHeritage is doing their best to rectify the situation and beef up security efforts, the doubt caused by the hack is understandably unsettling for affected users and potential consumers everywhere.
Walking the tightrope in an increasingly digital world
It’s no secret that today’s cyber-climate is more populated, dynamic, and personalized than ever before. The efficiency and customization that the online market offers are unparalleled. However, there is an underside to all this innovation that must be remembered. Service providers and their advertising teams are constantly looking for the most dynamic and personalized ways to advertise to their target markets in these online spaces.
This means collecting as much data on their consumers as possible and at whatever cost. Consumer’s digital fingerprints are increasingly valuable to companies across the digital market. If a company wants to get a consumer’s attention on the information highway, they know they need to personalize the experience as much as possible. This means that all the bits of data entered into your browser become fingerprints to help identify and sell to you.
In this competitive climate, genetic testing companies face an increased risk simply because of the personal nature of the data they collect. Having the genetic makeup of over 90 million consumers is an advertising goldmine, not to mention other potentially dangerous motivations of more malicious hackers. The bottom line? Users need to think twice and be vigilant about the data they choose to share.
“It’s a double-edged sword – EMR and genetic testing can help medicine,” Verger reiterates. “However, nothing out there is perfect,” Verger claims. “Things kept on servers can possibly be hacked or compromised and we need to remember that.”
Trying to find the right balance of technology risks and benefits? Wondering how to keep your organization current without succumbing to increased risk? Reach out to a team of seasoned IT security professionals.
A strategic IT partner will help improve your IT while managing and mitigating risk at the same time. You can have the best of both worlds – you just need a strategic partner, willing to walk the tightrope with caution and creativity.